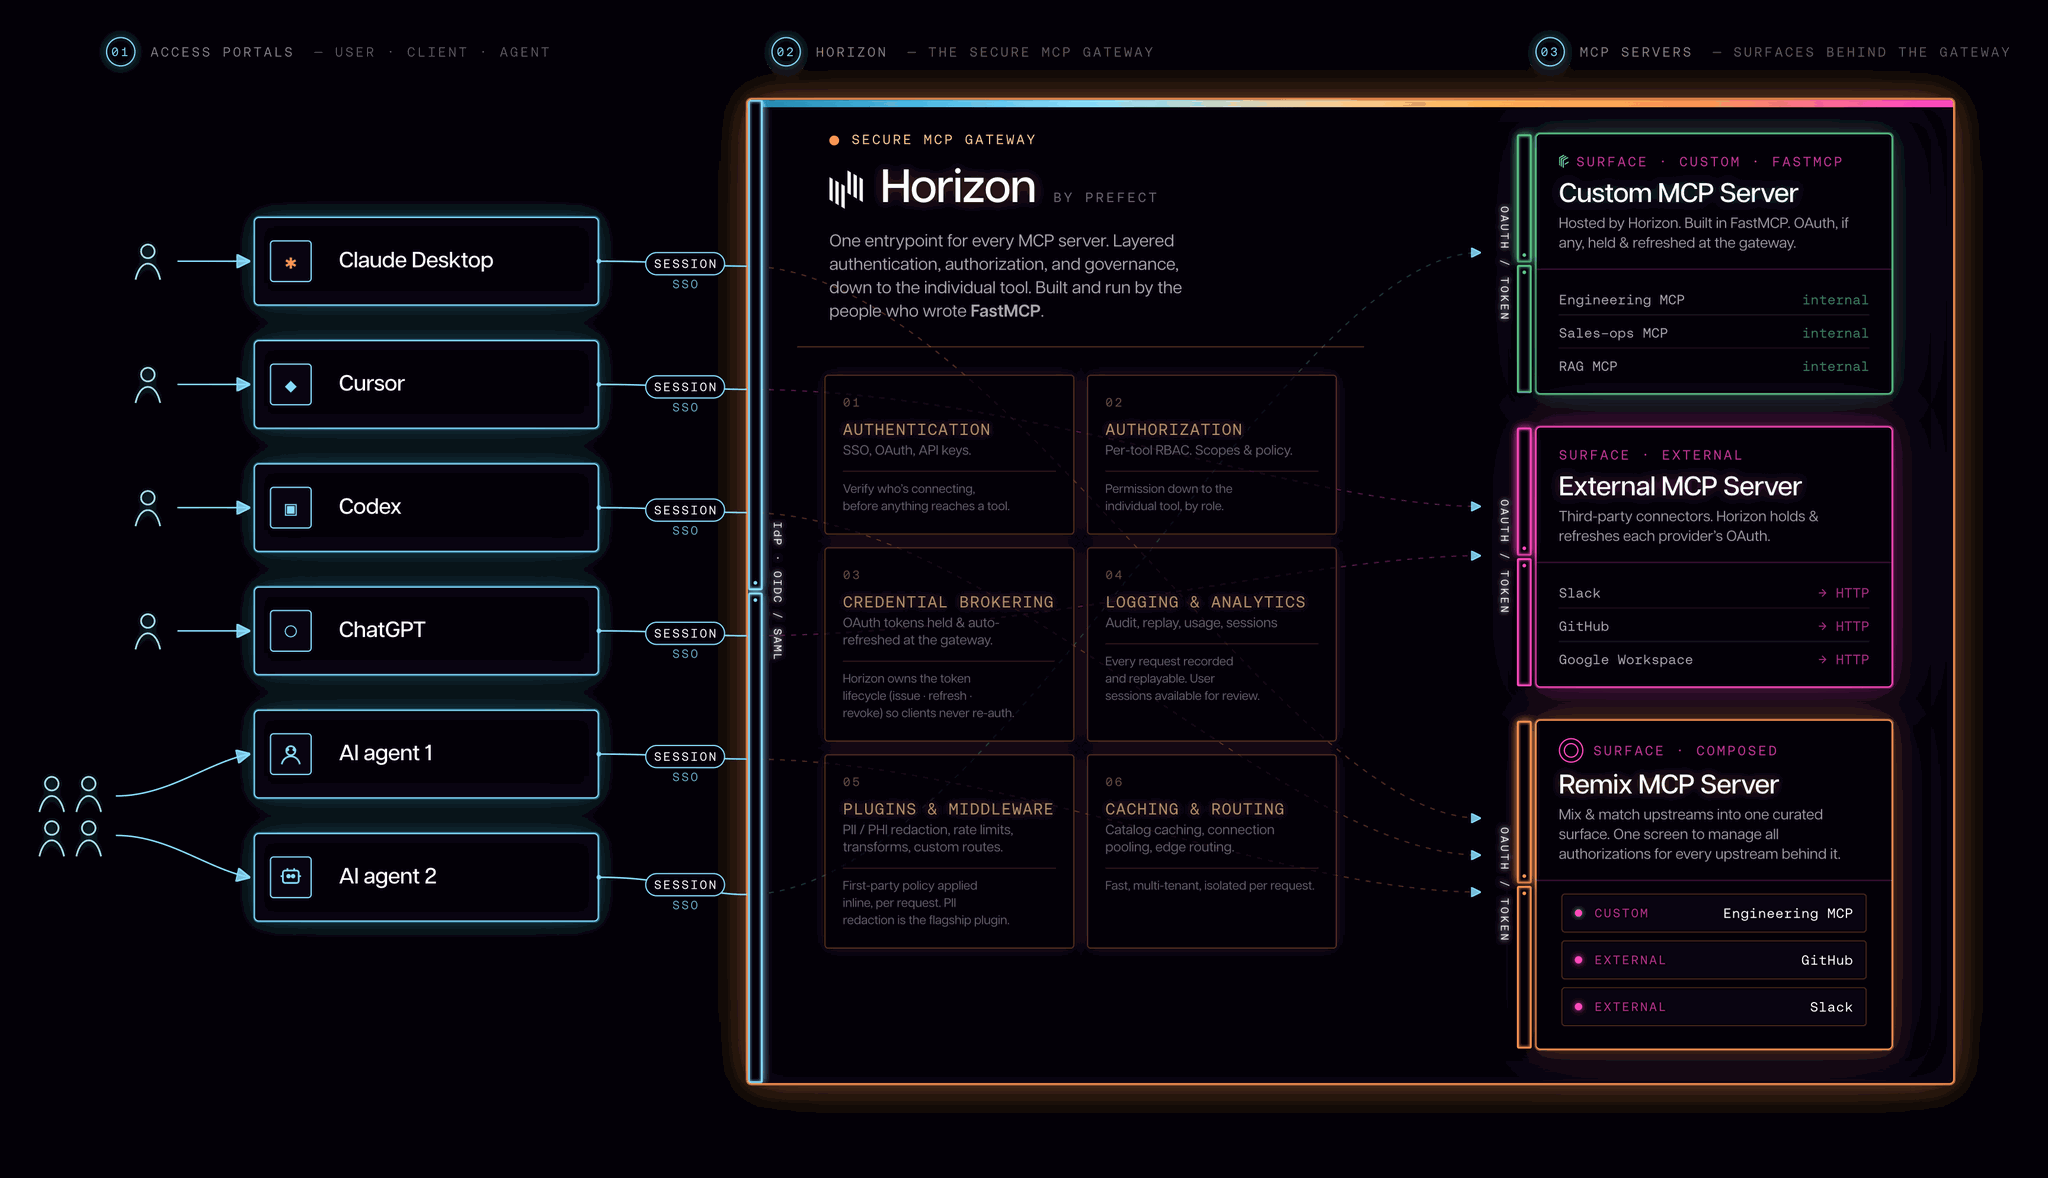
One entrypoint for every MCP server, with authentication, authorization, and governance enforced down to the individual tool.
MCP is spreading fast, and most teams are bolting servers onto their stack one at a time. Every new server is another set of credentials to manage, another surface to secure, another thing to audit. That sprawl gets dangerous quickly. FastMCP Gateway provides a single entry point for those servers.
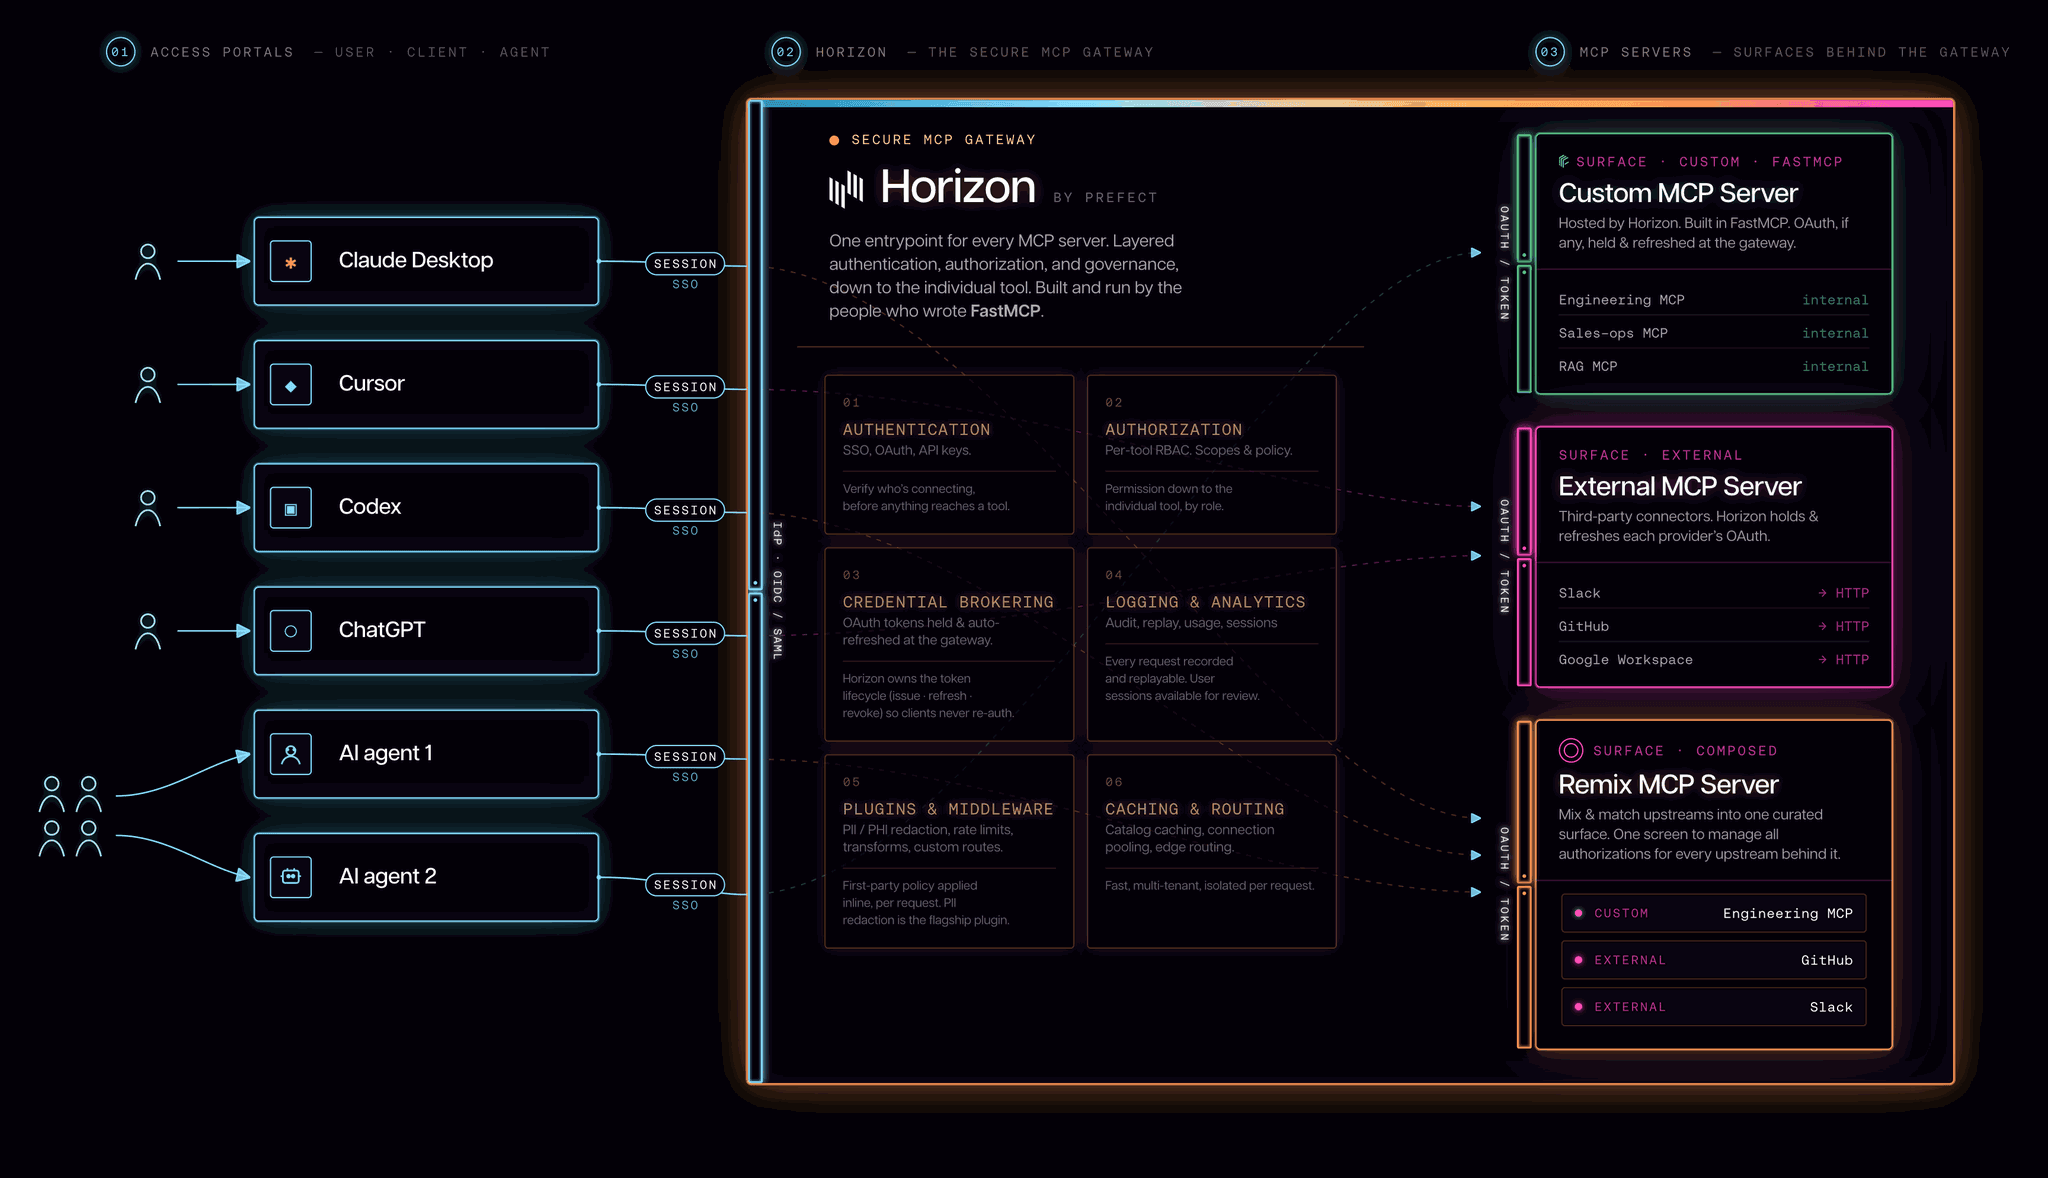
Every client connects to one place. Claude Desktop, Cursor, Codex, ChatGPT, your own AI agents. They authenticate once via SSO, OAuth, or API key, and our Gateway routes requests to the servers behind it. Authorization is enforced per tool with role-based scopes and policy, so a connected client only sees what its role allows. Credentials never leak to the client: the Gateway stores and auto-refreshes each upstream OAuth token, which means your clients never re-auth and your secrets never leave.
Behind the gateway, three kinds of surfaces. Custom servers you build in FastMCP and host on our Gateway. External third-party connectors like Slack, GitHub, and Google Workspace, where the Gateway manages each provider's OAuth for you. And Remix, where you mix and match upstreams into one curated surface and manage every authorization from a single screen.
Every request is logged, and attributable to a user session. This is the architecture that lets a regulated enterprise adopt MCP without handing the keys to every tool to every client. Built and run by the people who wrote FastMCP.
For the full picture, see the FastMCP Gateway overview.